The Fragment Is the New Attack Surface

September 17, 2026
•
1 min
Most security tools evaluate risk by looking at the file, but risk is no longer confined to files. A clause pasted into an AI prompt carries no filename. A table summarized into Slack carries no label. A screenshot dropped into a deck carries no metadata, yet none of these trip an alert, because legacy data loss prevention (DLP) was built for a world where the sensitive unit is a discrete object with a name, a location, and a policy attached to it. That world is gone. What replaced it does not look like a file leaving the building. It looks like a sentence, typed into a box that was never designed to hold it.
How the Landscape Shifted
The unit of risk has changed, and yet most programs still build controls for a version that no longer exists. The unit of risk used to be the file. Now it’s the fragment: a clause from a contract, a paragraph from a strategy doc, a chart screenshotted into a deck, moving through the organization with none of the markers a legacy tool was trained to look for.
None of those fragments move on their own. Instead, a workflow moves them. A research task folded into a draft, a data pull folded into a chat message, or an analyst pastes rows from a customer spreadsheet into ChatGPT as one step in reformatting a report. None of them think of it as moving sensitive data. They are just moving through their workflow, faster than before.
Every paste, summary, or screenshot strips away the filename and the classification tag, while leaving the sensitivity and its history fully intact. A DLP policy built to fire on a file path has nothing left to match against: the content survived, the evidence did not. Lifecycle matters more than location: the fix is protection that moves with the data as it changes shape, because a workflow will always outrun a control aimed at just one of its steps.
Why the Crossing Is Where Most AI-Era Leakage Happens
The easy story blames the AI tools. Block ChatGPT, restrict Claude, watch Copilot more closely. That story is convenient, and it is wrong. The real exposure happens the moment content moves from a governed system, like a file share or a CRM, into an ungoverned one, like a prompt box or a chat message. The AI tool is usually just where the fragment lands or leaves from. The crossing itself is what matters, and almost nobody is watching for it.
Agentic workflows run the same problem at machine speed. An agent that pulls a customer record, summarizes it, and hands that summary to a second agent is re-pasting and re-transforming sensitive content with no person in the loop to notice, and every step mints a new fragment along the way. Security programs that still ask which file an agent touched are asking a question that matters less with every passing month. The boundary belongs around the whole chain of actions an agent runs, from the first pull to the last handoff.
Fragment-Level Risk Needs Lineage
Basic classification answers one question well: what is this content labeled as? But, legacy classification says nothing about where that content came from or what happened to it since, and no rule set closes that gap.
What a fragment needs instead is data lineage, or a continuous record of where a piece of data originated and every transformation it passed through, paste, summary, screenshot, or rewrite, on the way to where it is now.
Lineage tells us where that text came from and what has happened to it since.
Reconstructing the path from source to current form is the only way to trace a pasted paragraph back to the contract it came from, once every identifying marker has already been stripped away.
What Lineage Means for DLP and AI Security Programs
For DLP and AI security programs, that shift has three practical implications:
- Audit what your DLP policies trigger on. A file type, a folder path, a fixed pattern: any one of those leaves a blind spot exactly where fragments live.
- Extend AI security coverage past the prompt submission to the paste and summarization steps that precede it. By the time a prompt is submitted, the sensitive content already made it in, and a summary of a confidential roadmap is still confidential even after none of the original sentences survive.
- Score fragments against their lineage instead of their current appearance. A paragraph with zero visible markers of sensitivity can still carry the full risk of the document it came from.
Why Fragment Risk Requires Data-Level Security
Network controls watch a boundary, and file-level controls watch an object, but neither watches the copy-paste itself, since that action is not a boundary or object. A clause typed into an AI application never hits a network chokepoint or becomes a file, so a policy built around either vantage point has nothing to inspect.
The fix has to live with the data itself, through every transformation that follows. Enforcement has to happen at the moment and location the action occurs: on the endpoint, in the browser, inside whatever AI tool is open. That means catching it as it happens, not reconstructing it later at a network chokepoint or in a post-incident review.
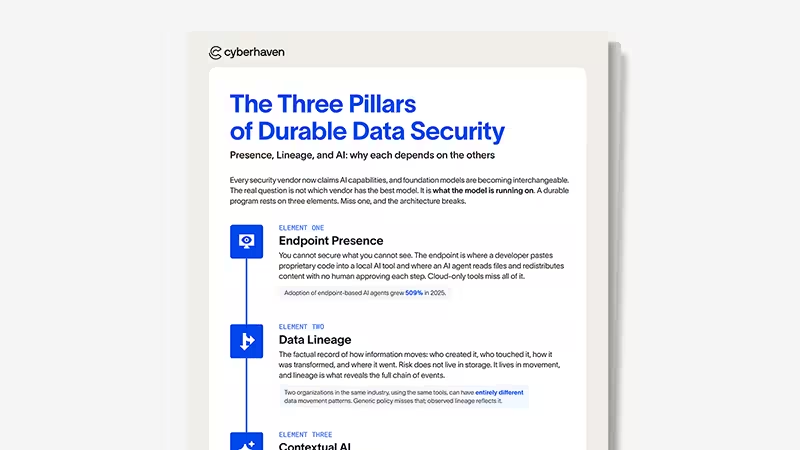
Data Lineage resolves a fragment back to the source it came from. Endpoint presence sees the paste happen in the first place. Together, that is data-level security: protection that travels with the content itself instead of waiting at a boundary the content may never cross.
For a deeper look at what this shift means for security programs built around agentic AI, see Governing The Agentic Enterprise.