Agentic Data Security: Control What AI Apps and Agents Do With Data

November 5, 2026
•
1 min
AI apps and agents are proliferating across enterprise endpoint environments as desktop apps, coding tools, and browser sessions. As I meet with CISOs and other security leaders, I consistently hear concern about the risk of AI agents accessing and exfiltrating sensitive data as well as performing harmful actions, maliciously or by mistake. But saying no to AI isn't an option. Employees want to use tools like Claude Cowork, Codex, and browser AI apps, and the challenge is how to allow that safely.
That's why we're introducing Agentic Data Security (ADS), the latest product in Cyberhaven Flow. ADS extends Data Security and Insider Risk protection for the Agentic Enterprise to AI apps and agents, building on the protection that the world's most innovative companies trust for their human workflows. It shows security teams what every agent does with sensitive corporate data and what actions the agent performs through commands and tools calls, thereby helping the enterprises stop sensitive data exfiltration and insider risk. Security teams can say yes to agents without losing control of their data.
How we built ADS also reflects our belief about where data security and insider risk is heading. We could have built a separate product for AI tools and agents than humans. But that would ignore how work gets done: humans and AI agents act in tandem across workflows on the endpoints, with data exfiltration and insider risk threats inter-mingled in human and AI tool interactions. A siloed tool that sees only part of a workflow produces a false sense of security. Instead, we built ADS on Cyberhaven Flow, which uses Data and Action Lineage combined with DLP, DSPM and Insider RIsk capabilities to secure human and agentic workflows end to end.
AI Apps and Agents Raise Data & Insider Risk
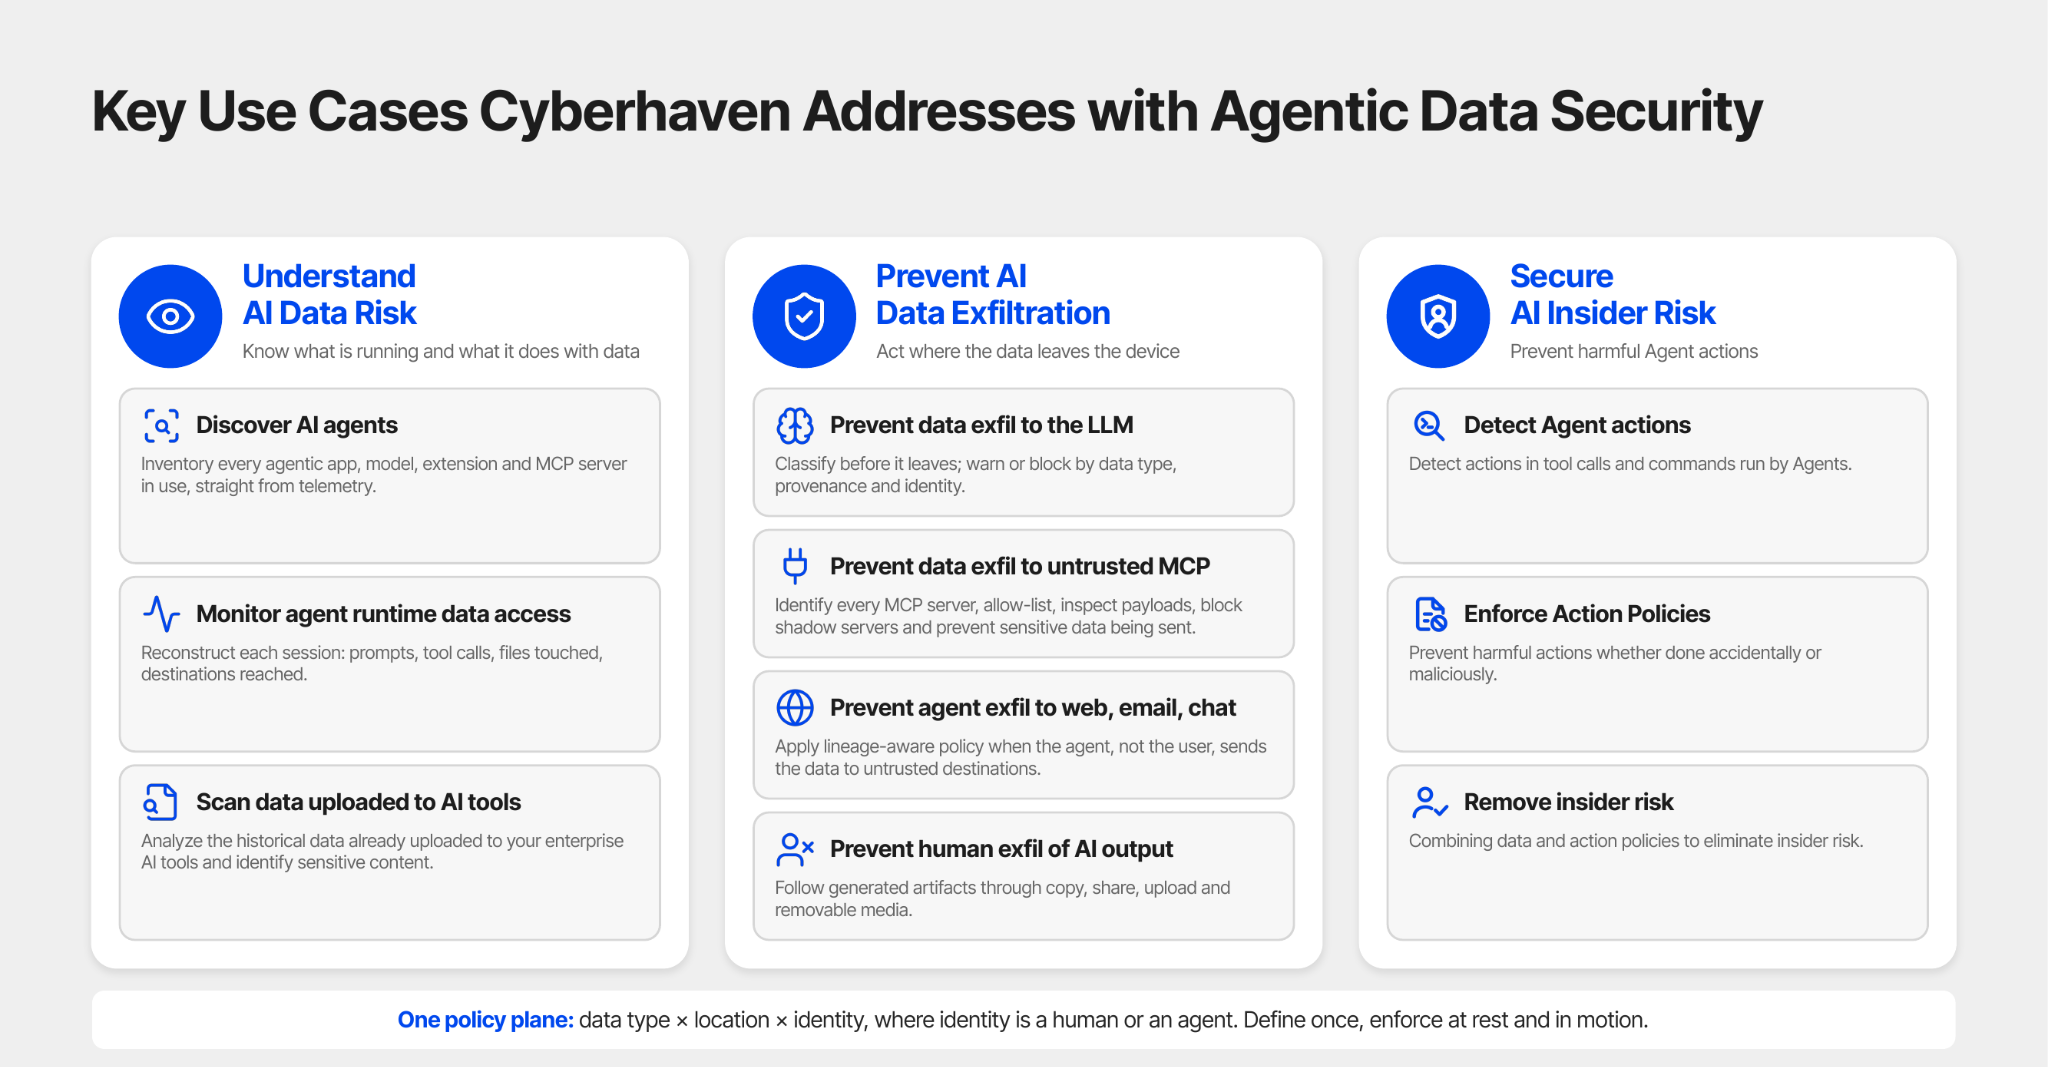
AI agents work with the (often privileged) access of the people or systems they serve. An agent can read files, call tools, and transform or share data in a single, near-instantaneous workflow. Agents act at machine speed and massive scale, often unsupervised, which creates greater data and insider risk than humans.
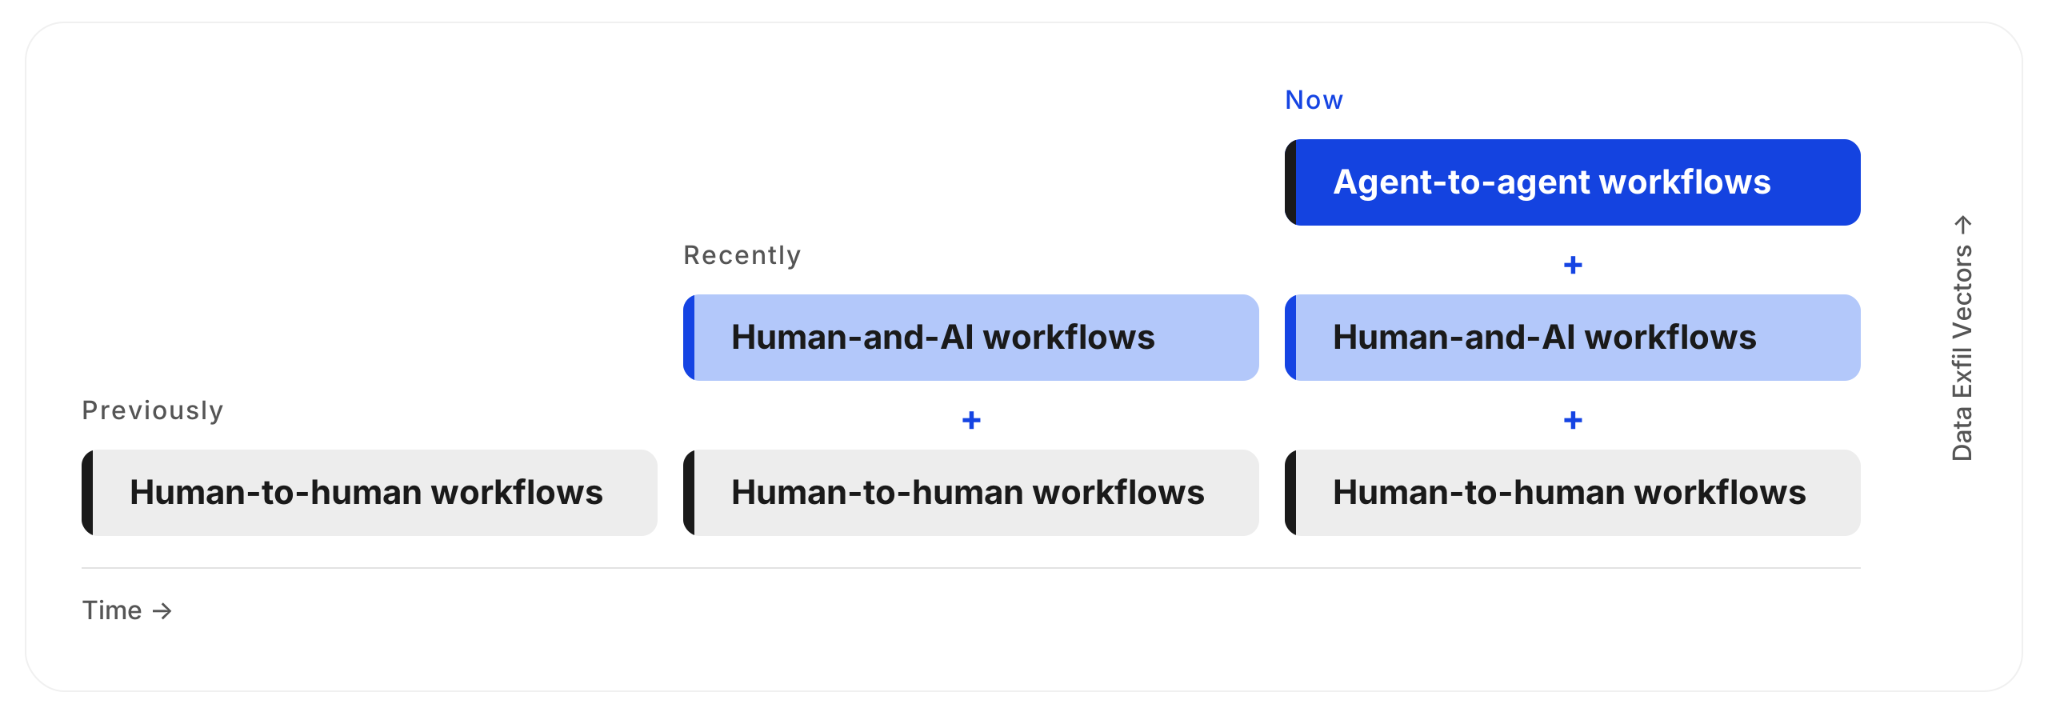
Exfiltration vectors also compound in the world of AI instead of replacing one another. AI apps and agents can send sensitive corporate data to LLMs, Model Context Protocol (MCP) servers (trusted or untrusted), the web, email, chat, and files saved to personal folders. Agents can execute privileged actions that can be harmful to the organization at machine speed.
Humans can also act along with AI to pose insider risk. A malicious user can take AI-generated output and exfiltrate it through traditional vectors such as upload, USB, or print. For example, an employee can ask an AI app to summarize or transform sensitive corporate information, save the result, and exfiltrate it later. These risks are growing: Cyberhaven Labs reports that endpoint-based adoption of agentic AI apps doubled between 2025 and 2026.
Why We Built Agent Protection on the Same Data Lineage
The way we work has changed. Work used to be human-to-human. It now includes human-to-AI and AI-to-AI workflows, so people, AI, and the two together are moving and transforming data in new ways. Securing data and removing insider risk in this world takes a platform that identifies these workflows, understands them, and applies controls for both humans and AI, whether the data is at rest or in motion.
After working with many of the world's most innovative companies, including frontier AI labs, aerospace companies, biotech firms, and major hedge funds, we consistently heard three things:
1. Workflows are the right focus for securing data. Data has always moved between people. Now it also moves between people and agents, and separate programs for humans and agents leave a gap at every handoff. Policies tied to a single channel lose the data the moment it moves.
2. An AI agent is a new kind of insider. A sensitive document is just as sensitive when an agent summarizes it as when an employee emails it, so policies should follow the data and its context, independent of the type of actor.
3. Customers want one place to manage data security and insider risk. They don't want to define classification and rules in one tool for data at rest, another for data in motion, and a third for agents. The complexity is the problem, and a new product adds to it.
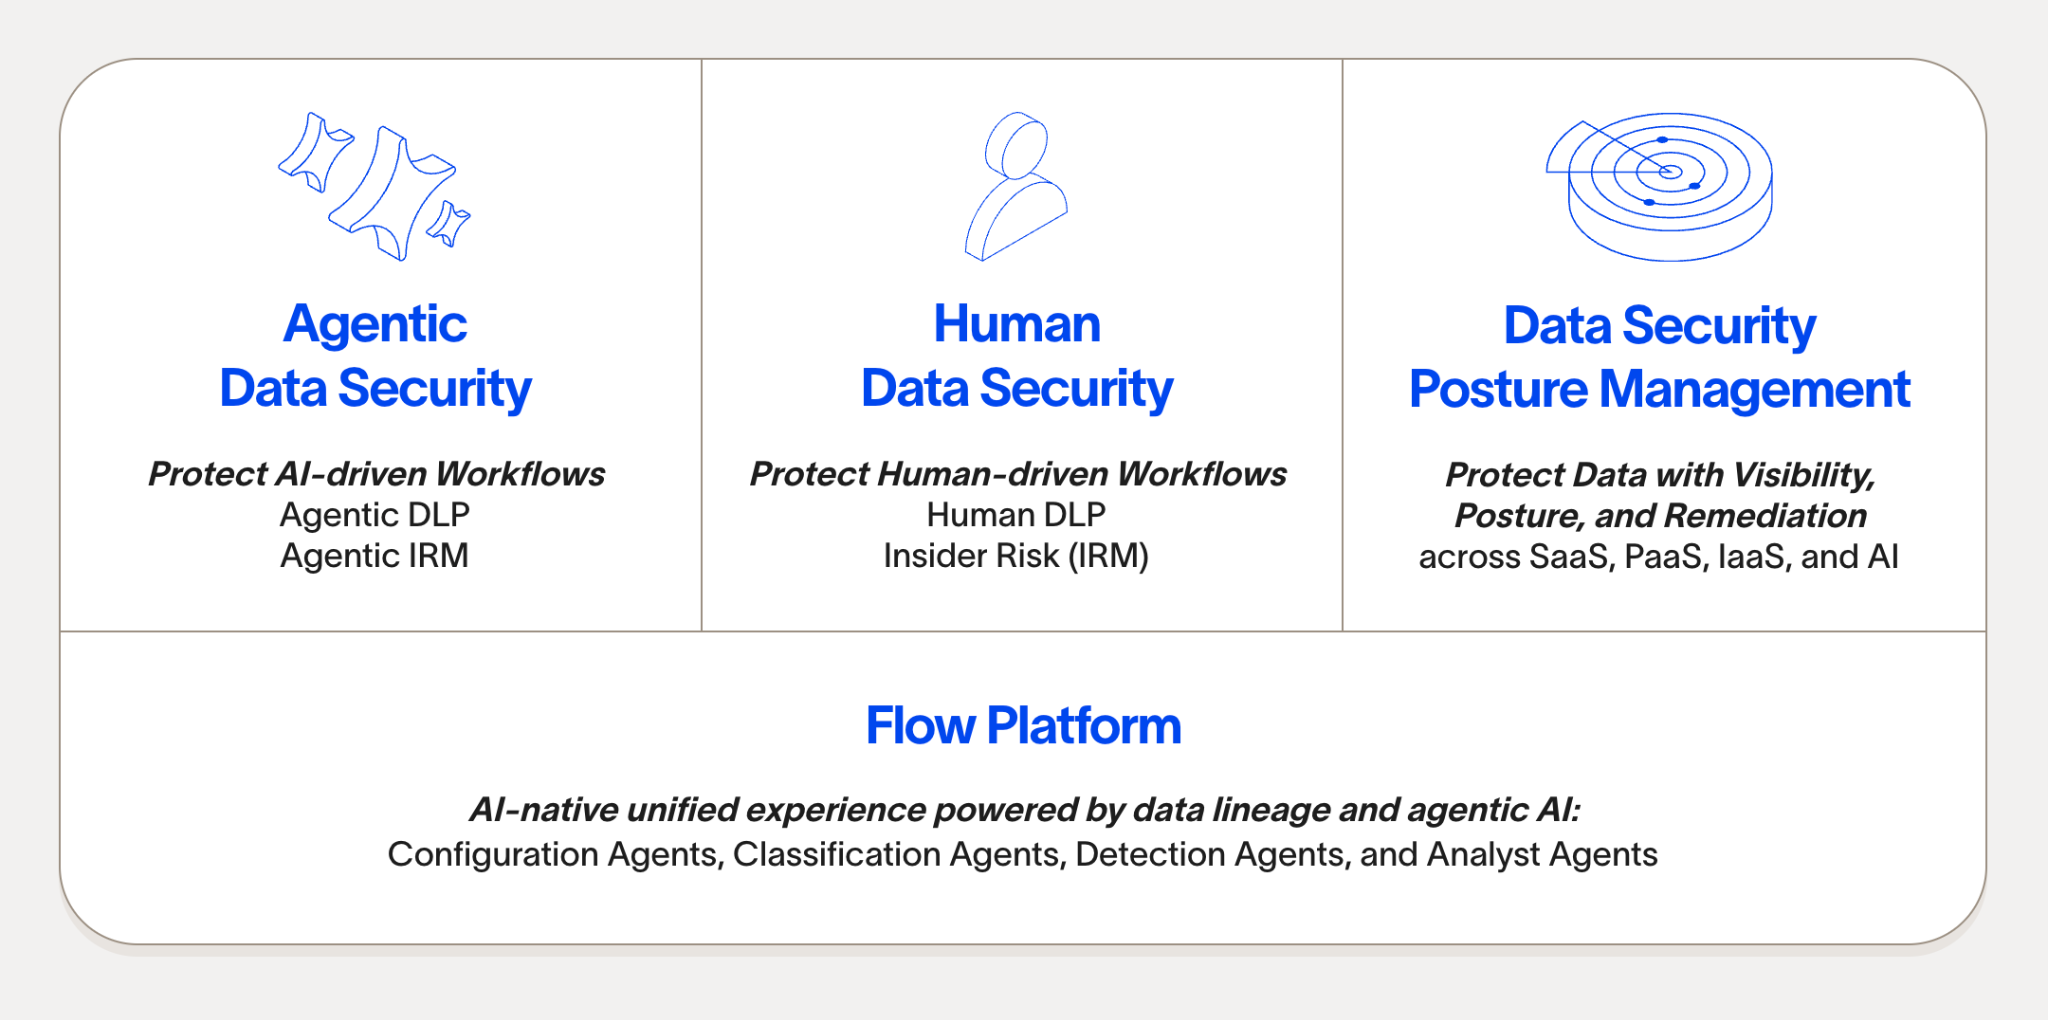
ADS joins Human Data Security and Data Security Posture Management (DSPM) in Cyberhaven Flow, which combines DSPM, insider risk management (IRM), and data loss prevention (DLP) in a single platform for people and agents. That lets enterprises reduce data exposure in the cloud, in AI apps, and in other repositories, and stop exfiltration from AI apps and agents at runtime on endpoints. Together, the products cover data at rest and in motion, for people and agents, on one data lineage.
Data Lineage traces data from origin through every move and transformation. Linea AI, our AI engine, adds an understanding of what the data is and how it's being used. This is the idea behind everything we build: Cyberhaven traces the full lifecycle of your data, adapting protection to changing context. When the tools in your environment change, or the next agent shows up, the intent behind your policies still holds.
How to Secure AI Adoption With Agentic Data Security
ADS enables data security and insider risk teams to extend protection to agentic workflows, find the risky workflows that threaten the business, and take action autonomously when and where it matters.
Find Agents Across the Environment
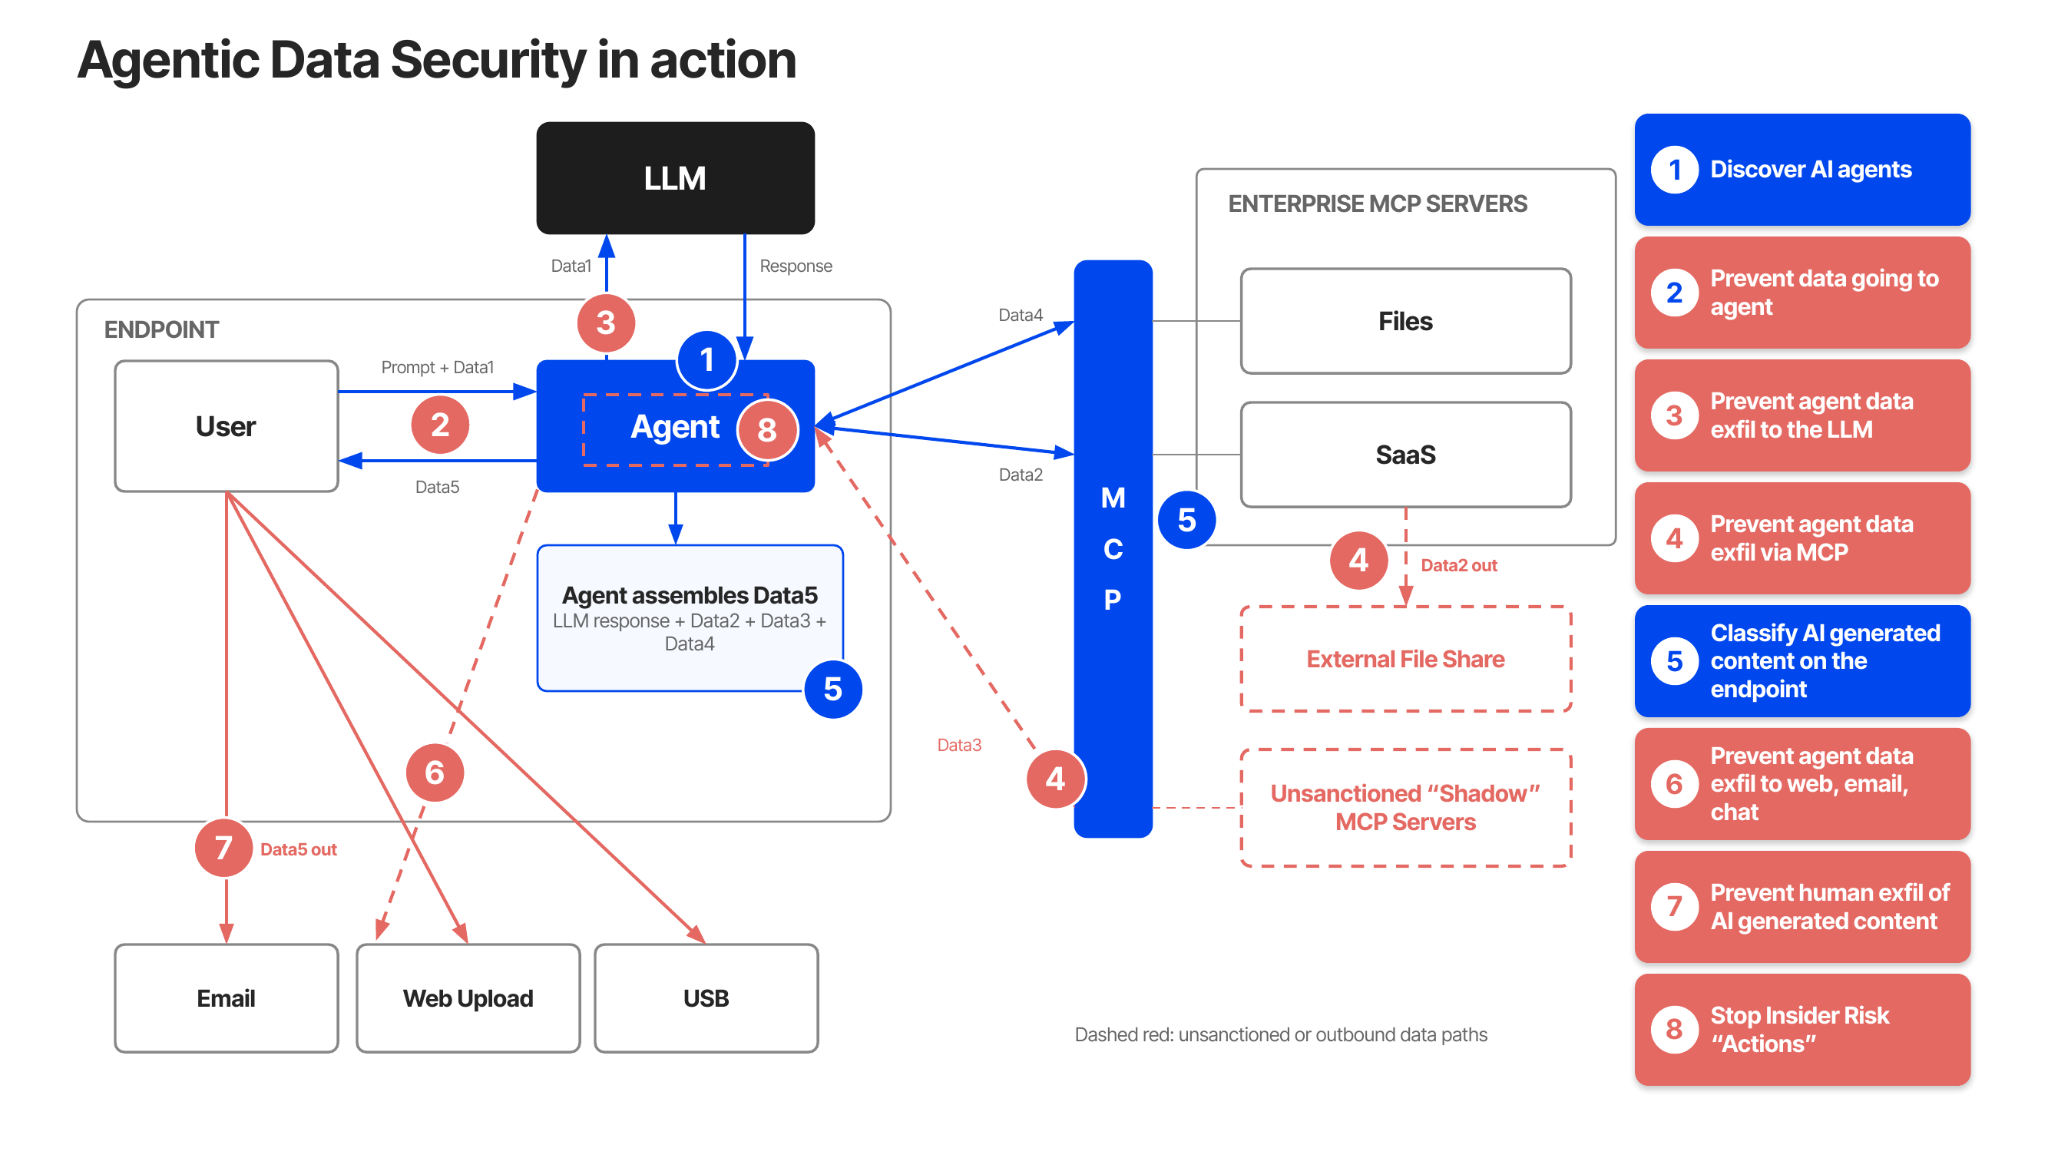
Discover AI tools and agents used across endpoints, whether they run as apps, as tools, or in browsers, including unsanctioned apps, and assess their risk. Cyberhaven inventories agentic applications on endpoints and detects the models, plans (free versus enterprise), extensions, and tools they use. It also monitors all MCP tool calls, whether over stdio or network.
See What Each Agent Does
Review prompts, responses, tool calls, file reads and writes, commands, and data destinations. ADS records the full AI conversation, including the data involved in each step and the actions, so investigators can follow an agent session as a workflow and see what actions the agent performed, how the data was transformed, and where it was sent.
See the Complete Human and AI Workflow
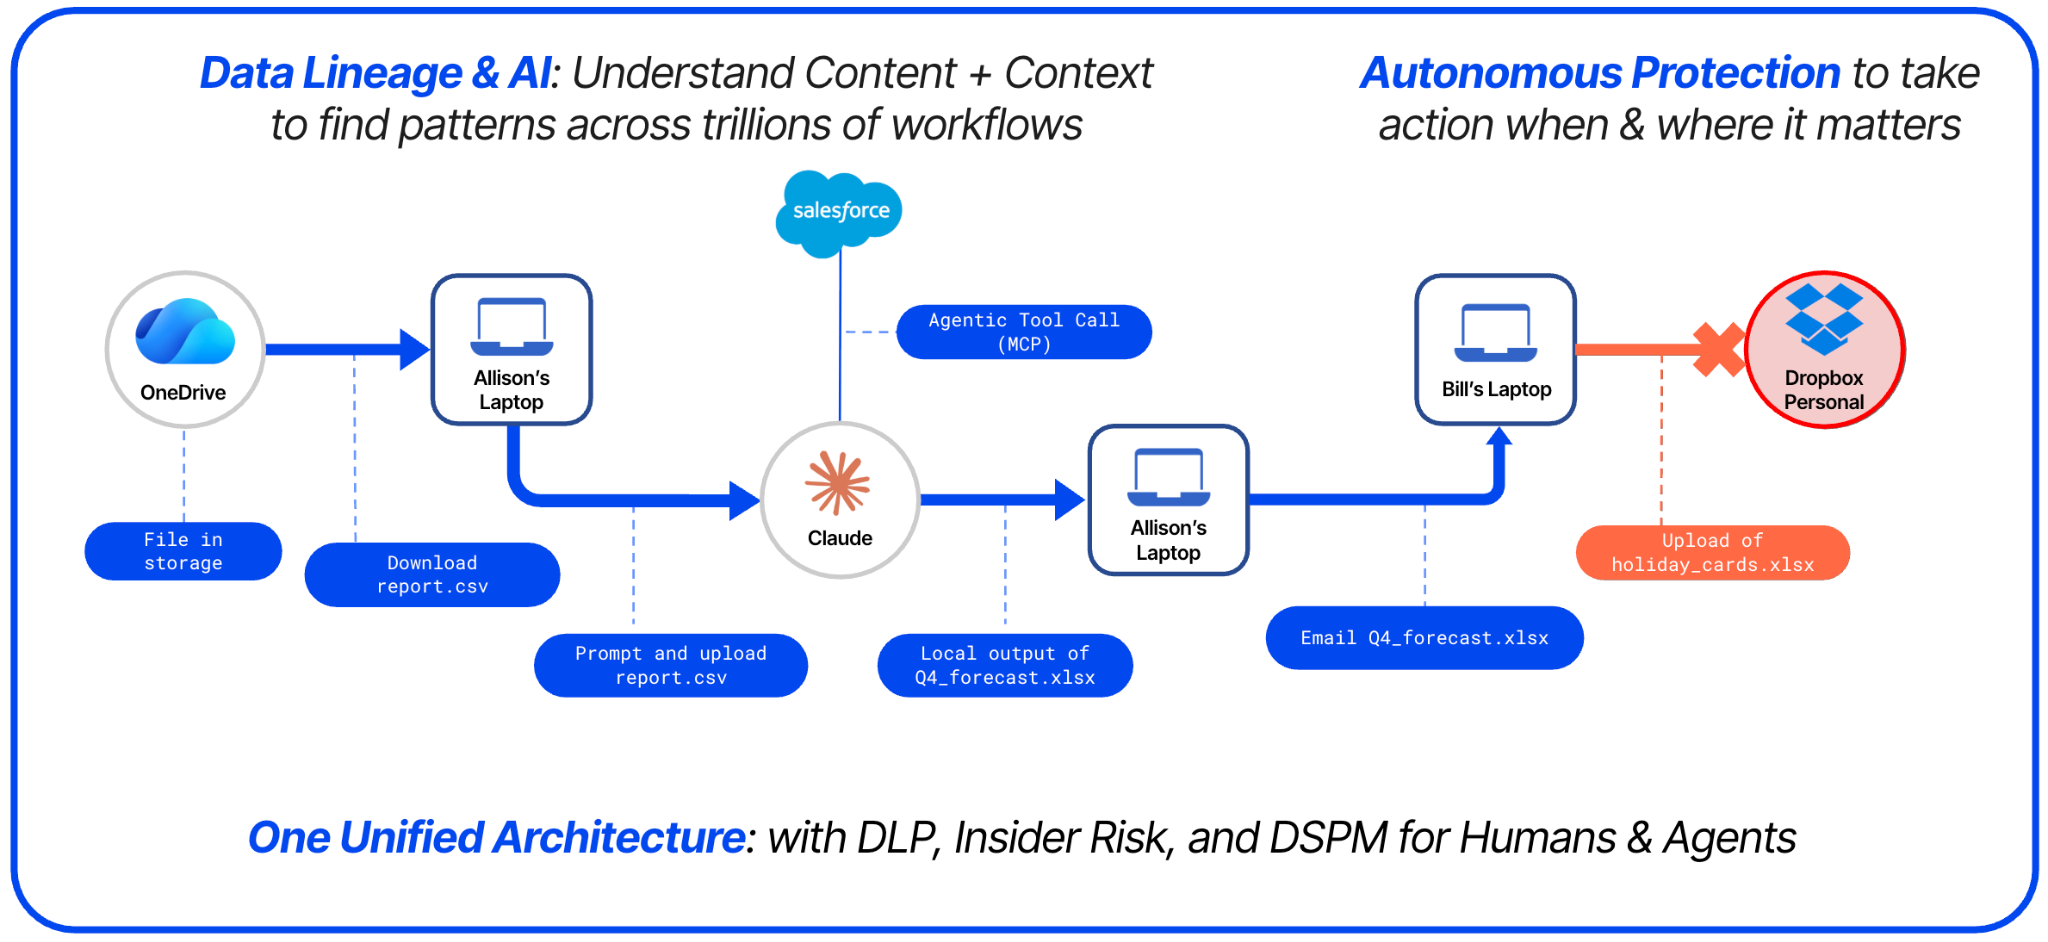
Tie each agent action to the person or system behind it, with people and agents visible together. Identity shows who initiated an action. Data Lineage shows what information the action touched and where it went next, including when a person picks that data up after the agent is done. Together, those details give security teams the context to investigate activity and assess risky data movement.
Detect Risky Agent Actions
Agents document their own work. Their tool calls and reasoning are recorded as they run, which makes them open to inspection like any other piece of content. ADS applies Cyberhaven's existing policy capabilities to that record to identify risky agent actions, the same way IRM flags risky behavior by people. It's how Cyberhaven delivers on its promise of DLP, IRM, and DSPM for both people and agents.
Stop Data Exfiltration
Apply existing data protection policies to agent actions, with context-aware warn or block controls for sensitive data and credentials. Corporate-versus-personal AI account controls and lineage-aware protections help prevent data exfiltration through agent workflows while teams continue to adopt AI.
Securing AI Apps and Agents Across the Enterprise
At enterprise scale, agents can arrive team by team, long before a central policy exists. Security and AI governance leaders need one view of sanctioned and unsanctioned tools, one record of what each agent did and how it accessed data, and protection that covers people and agents alike.
ADS brings agent inventory, activity records, identity attribution, and Data and Action Lineage into that one view. CISOs can stop sensitive IP and data from leaving, stop AI insider risk, investigate agent sessions, and bring a clear record to the board, GRC, and auditors. Frontier AI labs, top quant hedge funds, and highly regulated organizations already rely on Cyberhaven for their most sensitive data, and ADS extends that protection to agents.
Agents are already part of how your teams create, transform, and share data. Whether you're at the frontier of AI or just starting out, the answer is the same: protect the data itself, wherever it lives and goes. AI Changed Work. We Protect It.
Join the live executive briefing, “Double Trouble: Taking Control of Human & Agentic Insider Risk” on December 3, 11:30 AM CST.


Insights for the agentic enterprise
New guides, reports, and insights on data security, sent as they publish.